Marketing

Email Deliverability: SPF, DKIM, DMARC and List Hygiene

Antonio Evans10 min read

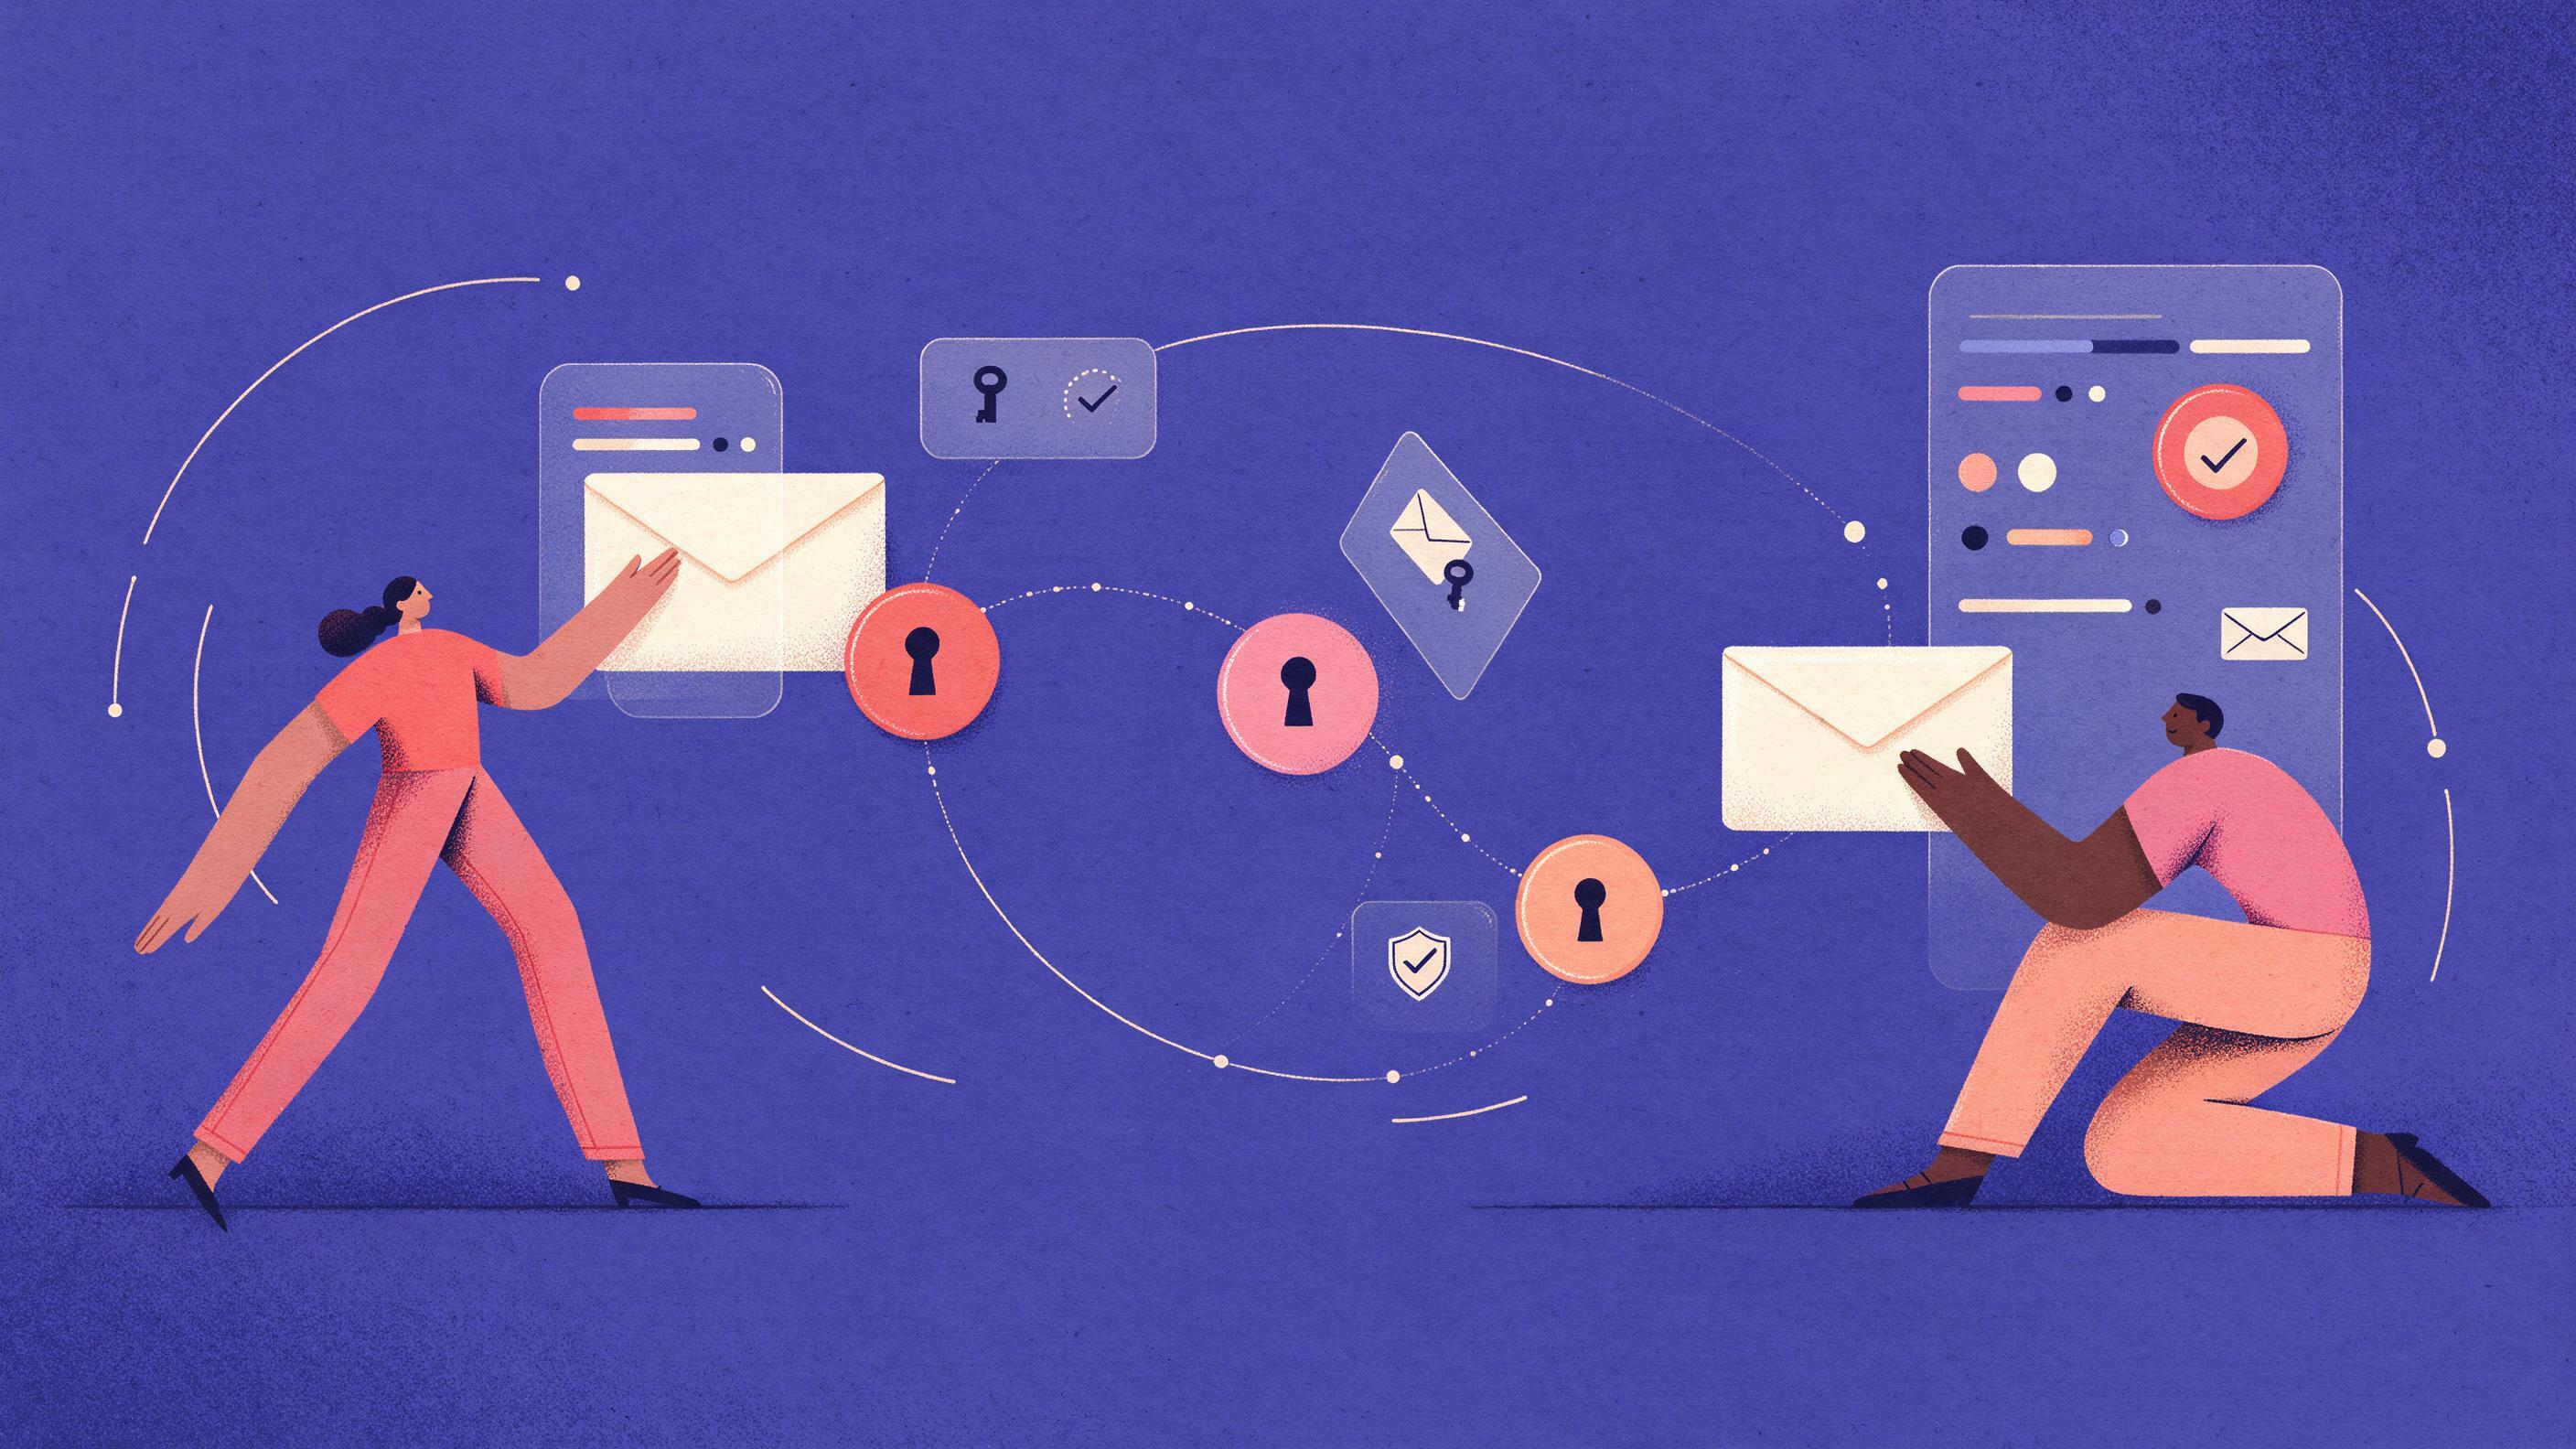
A technical diagram showing the path of an email from sender to inbox, with three checkpoints labeled SPF, DKIM and DMARC.
Key points

Key points

  1. 1Set up SPF, DKIM and DMARC on a dedicated sending subdomain so that your transactional mail keeps its own reputation separate from your newsletter.
  2. 2Keep DMARC at p=none while you read aggregate reports, then move to quarantine and reject only after every legitimate sender passes alignment.
  3. 3Prune hard bounces immediately, retry soft bounces on a schedule, and suppress any address that complains more than once.
  4. 4Watch your spam complaint rate against the 0.1 percent working ceiling and the 0.3 percent hard policy line that Gmail and Yahoo publish.

Start with a dedicated sending subdomain

Before you touch a single DNS record, decide which domain will carry the From header. Sending from your root domain (example.com) mixes newsletter reputation with the reputation of password resets, invoices and receipts. A separate subdomain such as news.example.com or mail.example.com keeps the pieces apart, and Yahoo explicitly recommends segregating the types of email you send by IP or by DKIM domain, because each IP and DKIM domain carries its own reputation (Yahoo Sender Hub).

The same logic applies inside a campaign system. Gmail counts all messages from the same primary domain toward its bulk threshold, so 2,500 messages from example.com plus 2,500 from promotions.example.com still add up to 5,000 and classify you as a bulk sender permanently (Gmail sender guidelines FAQ). A dedicated subdomain does not exempt you from the rules, but it does let you measure and fix one stream without dragging the others down.

Three habits make this work in practice:

  1. Pick one subdomain for marketing, newsletter and lifecycle campaigns. Name it something you will still recognize in an audit, like mail.example.com or go.example.com.
  2. Leave transactional mail (order confirmations, password resets) on a second subdomain or a separate provider, so a bad campaign cannot poison receipts.
  3. Record every host that sends on your behalf in a single inventory document. Assignment, the CRM, the support desk, the invoicing tool and any agency all count.

That inventory is the input to everything below. Without it, you will publish records that omit a legitimate sender, and your first DMARC enforcement step will start rejecting real business mail.

SPF: publish only the senders that are really yours

An SPF record is a TXT record at the root of the sending domain that lists the servers, IP addresses and include mechanisms allowed to send mail for that domain. Receivers look it up against the envelope sender (the Return-Path), not the visible From header, which is exactly why SPF alone cannot stop a spoof of the From address (Valimail).

A working record usually looks like this:

mail.example.com.  3600  IN  TXT  "v=spf1 include:_spf.provider-a.com include:_spf.provider-b.com -all"

Two design points matter more than the syntax. First, the total number of DNS lookups the record triggers is limited to 10; once you include several vendors, each of which includes more domains, you can exceed the limit and cause a permerror. That is a common cause of "SPF fails only sometimes" tickets. Second, use -all (hard fail) rather than ~all (soft fail) once you have verified the inventory, because soft fail gives receivers a weaker signal.

Check the record with a public lookup tool after every change, and check again after any vendor migrates infrastructure. Providers do change IP ranges, and an SPF record that references a stale range silently fails for a portion of your mail.

DKIM: sign every message and publish the public key

DKIM attaches a cryptographic signature to each message. The sending system holds the private key and signs selected headers and the body; the public key sits in DNS at a selector you choose, so receivers can verify both that the message came from someone holding the key and that it was not altered in transit (Valimail). Yahoo asks for a minimum key length of 1024 bits and notes that signatures let the receiver associate mail with the signer and confirm the content has not changed (Yahoo Sender Hub).

Setup is usually a copy and paste job inside your email platform:

  1. Generate a key pair in the platform (most providers do this for you) and pick a selector such as s1 or mail.
  2. Publish the TXT record the platform gives you at selector._domainkey.yourdomain, for example s1._domainkey.mail.example.com.
  3. Send a test message to a Gmail address you control and inspect the original. You want dkim=pass with the domain matching your sending subdomain.
  4. Rotate keys on a documented schedule and keep the old public key published for a grace period so in-flight mail still verifies.

DKIM is the record most likely to survive forwarding, because it signs content rather than the envelope. It can still break when a mailing list rewrites headers or the body, another reason SPF and DKIM are complements rather than alternatives.

DMARC: alignment is the part people get wrong

DMARC is a TXT record at _dmarc.yourdomain that tells receivers what to do when a message fails authentication, and it adds reporting. The allowed policies are none (take no action), quarantine (send to spam) and reject (refuse delivery) (Google Workspace Help).

The concept that decides whether DMARC actually works for you is alignment. DMARC passes only if an authenticated identifier matches the domain in the visible From header. With relaxed alignment (the default), a subdomain of your organizational domain matches. With strict alignment, the domains must match exactly (Adaptive Security). This is where third-party senders cause trouble: an ESP that signs DKIM with its own domain, or rewrites the Return-Path, will authenticate the message but fail alignment for yourdomain, so DMARC fails anyway.

A conservative starting record:

_dmarc.example.com.  3600  IN  TXT  "v=DMARC1; p=none; rua=mailto:[email protected]; ruf=mailto:[email protected]; pct=100; adkim=r; aspf=r"

Then progress in three stages, and do not skip the first:

StagePolicyWhat you are doingExit condition
Monitorp=none with rua reportingCollecting aggregate reports from Gmail, Yahoo, Microsoft and others30 days of reports where every legitimate source passes SPF or DKIM alignment
Quarantinep=quarantine, optionally pct=25 rising to 100Failing mail goes to spam instead of the inboxNo unexplained failures from known senders for two reporting cycles
Enforcep=rejectFailing mail is refusedSteady state; revisit only when you add a new sending vendor

Bulk senders must publish a valid DMARC policy with at least p=none, must include an rua tag so reports actually arrive, and must ensure the From domain aligns with either SPF or DKIM; relaxed alignment is acceptable (Yahoo Sender Hub). Gmail's rule set is the same shape: SPF, DKIM and DMARC for bulk senders, SPF or DKIM for everyone else, and From alignment with the SPF or DKIM domain (Gmail Help). AWS summarized the shift as three buckets: stricter domain authentication, easy unsubscribe, and complaint rates below 0.3 percent (AWS Messaging blog).

Read your aggregate reports before you enforce. They are XML files, so use a free parser or your ESP's DMARC dashboard. Look for two things: sources you did not know about (fix by adding them to SPF or moving them to your DKIM domain), and forwarders that break alignment (fix with ARC, which Yahoo recommends for forwarders, or by accepting that forwarded mail may fail).

A worked example with numbers

Say your list is 40,000 subscribers and you send four campaigns a month, so 160,000 messages monthly to personal Gmail accounts, or roughly 5,300 a day averaged across the month. You are over the 5,000-per-day line, so you are a bulk sender.

Now suppose 1 percent of that monthly volume fails DMARC alignment because an old CRM instance is still sending with its own Return-Path. That is 1,600 messages a month landing in spam or being rejected once you enforce, including password resets and order confirmations to customers who think you have gone silent. On the sending subdomain alone, 400 newsletter messages a month (1 percent of 160,000 is 1,600 total; if a quarter of that is newsletter traffic, 400) would disappear. Fixing the CRM record costs one DNS change. That is the entire argument for staged enforcement.

Bounce handling: hard, soft and the suppression list

Bounces are not all equal, and treating them the same is how lists rot.

  • Hard bounce: the address does not exist or the domain refuses mail permanently. Remove it from all active sending immediately and never mail it again. Repeatedly hitting dead addresses is a classic spam signal.
  • Soft bounce: a temporary failure such as a full mailbox, a greylisted server or a timeout. Retry on a schedule, typically a few attempts over 24 to 72 hours, then move the address to a hold status rather than deleting it.
  • Block bounce: the receiving server refused the message for policy reasons. Investigate reputation before you retry.

For context on normal rates, Mailchimp publishes average bounce and complaint figures by industry alongside open and click rates, and its all-user averages show open rate around 35.6 percent and click rate around 2.6 percent (Mailchimp benchmarks). Use those as a sanity check, not a target, since open rates are inflated by privacy features that preload images. Clicks and replies are the honest engagement signals, as Letterhead notes when it argues open rates have become a directional signal rather than a precise measure (Letterhead).

A simple suppression policy that holds up under scrutiny:

  1. Hard bounce: suppress after the first permanent failure.
  2. Soft bounce: retry three times across 72 hours, then suppress.
  3. Complaint (spam button): suppress after the first complaint, no exceptions.
  4. Unsubscribe: honor within two days, which is what Yahoo requires (Yahoo Sender Hub).

Complaint rates: the number that gets you filtered

Gmail and Yahoo both publish a hard threshold: keep spam complaint rates reported in Postmaster Tools below 0.3 percent, or risk rejections and spam placement (Gmail Help). Yahoo states the same 0.3 percent ceiling and adds that its calculation is based on mail delivered to the inbox, not total mail sent (Yahoo Sender Hub).

Operators who work with the Postmaster dashboard daily recommend a lower working ceiling of 0.1 percent, with 0.1 to 0.3 percent treated as a warning band and anything above 0.3 percent handled as a reputation incident (Suped). The dashboard measures manual spam reports on inboxed mail to personal Gmail accounts, is delayed, and can show gaps on low-volume days, so a single bad reading is not proof of a crisis.

Here is the arithmetic that makes the threshold matter. If you send 20,000 messages to Gmail inboxes in a month, 0.1 percent is 20 complaints and 0.3 percent is 60. Twenty complaints across a month is roughly five a week. A single poorly targeted campaign to a re-engaged segment can generate that in an hour. Track the rate per campaign and per segment, not just monthly, or you will see the spike after the damage.

Google's Postmaster Tools now includes a compliance status view where you can check whether your domain meets the bulk sender requirements, which pairs with the spam rate dashboard (Gmail sender guidelines FAQ). Register your sending domain there on day one.

List hygiene: signup, pruning and re-permission

Authentication gets you into the inbox. List quality keeps you there. Three processes do most of the work.

Validate at signup. Use double opt-in or at minimum an email verification step. Do not sign people up with a pre-checked box; Yahoo explicitly flags purchased lists and pre-checked opt-in boxes as practices to avoid (Yahoo Sender Hub). Watch for role addresses (info@, sales@) and known disposable domains, and require the confirmation click to be an actual action rather than an automated scan.

Prune on a schedule. Define engagement windows that match your cadence. A newsletter that sends weekly might keep addresses engaged in the past 180 days and move the rest to a monthly digest or re-permission campaign. A quarterly sender needs a longer window. Then:

  1. Identify subscribers with zero opens and zero clicks over the window.
  2. Send a short re-permission email with a single clear action ("keep receiving this, click here").
  3. Suppress anyone who does not respond within two weeks.
  4. Never re-add suppressed addresses, including via a new import.

Segment by engagement at send time. When you mail your most recent engagers first and your dormant tail last (or not at all), you keep complaint rates low on the segment most likely to complain. This is the same segmentation logic that industry guides put first in any list-building list, and the payoff is measurable in complaint rate rather than open rate.

The growth tactics that fill a list matter here too, because a list built on giveaways and popups carries lower intent. Guides to newsletter growth that emphasize a narrow reader and a clear promise produce cleaner lists than broad lead-magnet campaigns, and the result shows up as fewer complaints per thousand sends (Founderpath).

Monitoring and the operational checklist

Set up a weekly review that takes fifteen minutes and covers five numbers: complaint rate in Postmaster Tools for each sending domain, hard and soft bounce rates from your ESP, DMARC aggregate report failures by source, click rate per campaign, and unsubscribe rate. Then run this checklist before you change any DNS record.

CheckToolPass condition
SPF record resolves and stays under 10 lookupsPublic DNS lookup toolNo permerror, -all present
DKIM signs with the From domainSend a test, inspect headersdkim=pass and domain matches sending subdomain
DMARC report mailbox is receivingrua inboxReports arriving daily from major providers
Postmaster domain verifiedPostmaster ToolsDomain listed, spam rate visible
Suppression list appliedESP settingsHard bounces and complaints suppressed on send
One-click unsubscribe presentInspect headersList-Unsubscribe with the post method
Reverse DNS on sending IPsDNS lookupPTR record matches the sending hostname

That last row matters more than most people expect: Gmail requires all senders to have SPF or DKIM plus valid forward and reverse DNS records, and bulk senders to have both (Gmail Help). If you send through a shared ESP you do not control the PTR, which is another reason to use a reputable provider and to verify its hostnames rather than assume.

When you need to test all of this at once, run a seed test. Send the campaign to a handful of addresses across Gmail, Outlook, Yahoo and Apple, then read the raw headers for each. You are checking for pass results on each authentication method and alignment to your From domain. A seed test takes minutes and catches most misconfigurations before a real campaign does.

If the operational side is not where you want your engineering hours to go, describe the setup you need and let a specialist build it with you at Quanta. The work is a checklist, not a research project, but the DNS records have to be right the first time you enforce.

FAQ

FAQ

How long should I stay at p=none before enforcing DMARC?

Give it at least one full reporting cycle with enough volume for meaningful data, and usually 30 days or more. The exit condition is not time; it is a clean set of aggregate reports where every legitimate sending source passes SPF or DKIM alignment. Move to quarantine only after that, and to reject only after quarantine produces no unexplained failures.

We send under 5,000 messages a day. Do the Gmail and Yahoo bulk rules apply?

Gmail's bulk requirements kick in near 5,000 messages per day to personal Gmail accounts from the same primary domain, and once you are classified as a bulk sender the status is permanent (Gmail sender guidelines FAQ). Below that line, all senders still need SPF or DKIM, valid forward and reverse DNS, and a spam rate below 0.3 percent (Gmail Help). The requirements only get stricter as volume rises, so build to the bulk standard regardless.

What actually counts as a spam complaint for the 0.3 percent threshold?

It is the recipient pressing the spam button, not Gmail's automatic filtering decision. Gmail calculates the rate on mail that reached the inbox for users included in its calculation, and Yahoo says the same about its own measurement (Yahoo Sender Hub). That means your ESP's complaint number and Postmaster's number will differ. Use Postmaster for the Gmail view and your ESP for the rest, and treat 0.1 percent as the working ceiling rather than the policy line (Suped).

Should I delete hard bounces or just stop mailing them?

Stop mailing them, and keep the record with a suppression flag rather than deleting it. If you delete, a well-meaning import months later can bring the address back. A suppression flag survives imports and lets you reproduce why the address was removed if a customer asks. Merge or replace your suppression list only when you can prove the replacement contains every previously suppressed address.

Our email passes SPF and DKIM but DMARC still fails. Why?

This is the alignment problem. SPF checks the envelope sender and DKIM verifies the signing domain, but DMARC requires one of those to match the domain in the visible From header. A third-party sender that rewrites the Return-Path or signs with its own domain will authenticate but not align (Adaptive Security). The fix is either to move that sender onto your DKIM domain and selector, or to count it as a known source in your reporting before you enforce.

Sources

Sources

  1. Sender Best Practices - Yahoo Sender Hub
  2. Email sender guidelines FAQ - Gmail Help
  3. SPF, DKIM, and DMARC authentication: How they work ...
  4. Set up DMARC | Security & data protection
  5. What Is DMARC Alignment? SPF, DKIM, and Strict Modes
  6. Email sender guidelines - Gmail Help
  7. An Overview of Bulk Sender Changes at Yahoo/Gmail - AWS
  8. Email Marketing Benchmarks & Industry Statistics - Mailchimp
  9. Newsletter Open Rate Benchmarks: A Modern Guide - Letterhead
  10. Understanding Google Postmaster Tools V2 Spam Rate ...
  11. Newsletter Growth Strategy: 30 Tactics to Reach 10K Subscribers
About the author

About the author

Antonio Evans
Antonio Evans

Antonio Evans is the founder of Quanta Intelligence and a fractional CTO who builds HIPAA-ready AI systems for health and life-science companies. Before that he was technical co-founder of FriendsEAT for twenty years, CEO of Socialdraft, and a data engineer at IBM. Antonio lives with his dog Santino in Lisbon, Portugal.

All articles