Security

How to Run a Quarterly Access Review for a Small Team

Antonio Evans10 min read

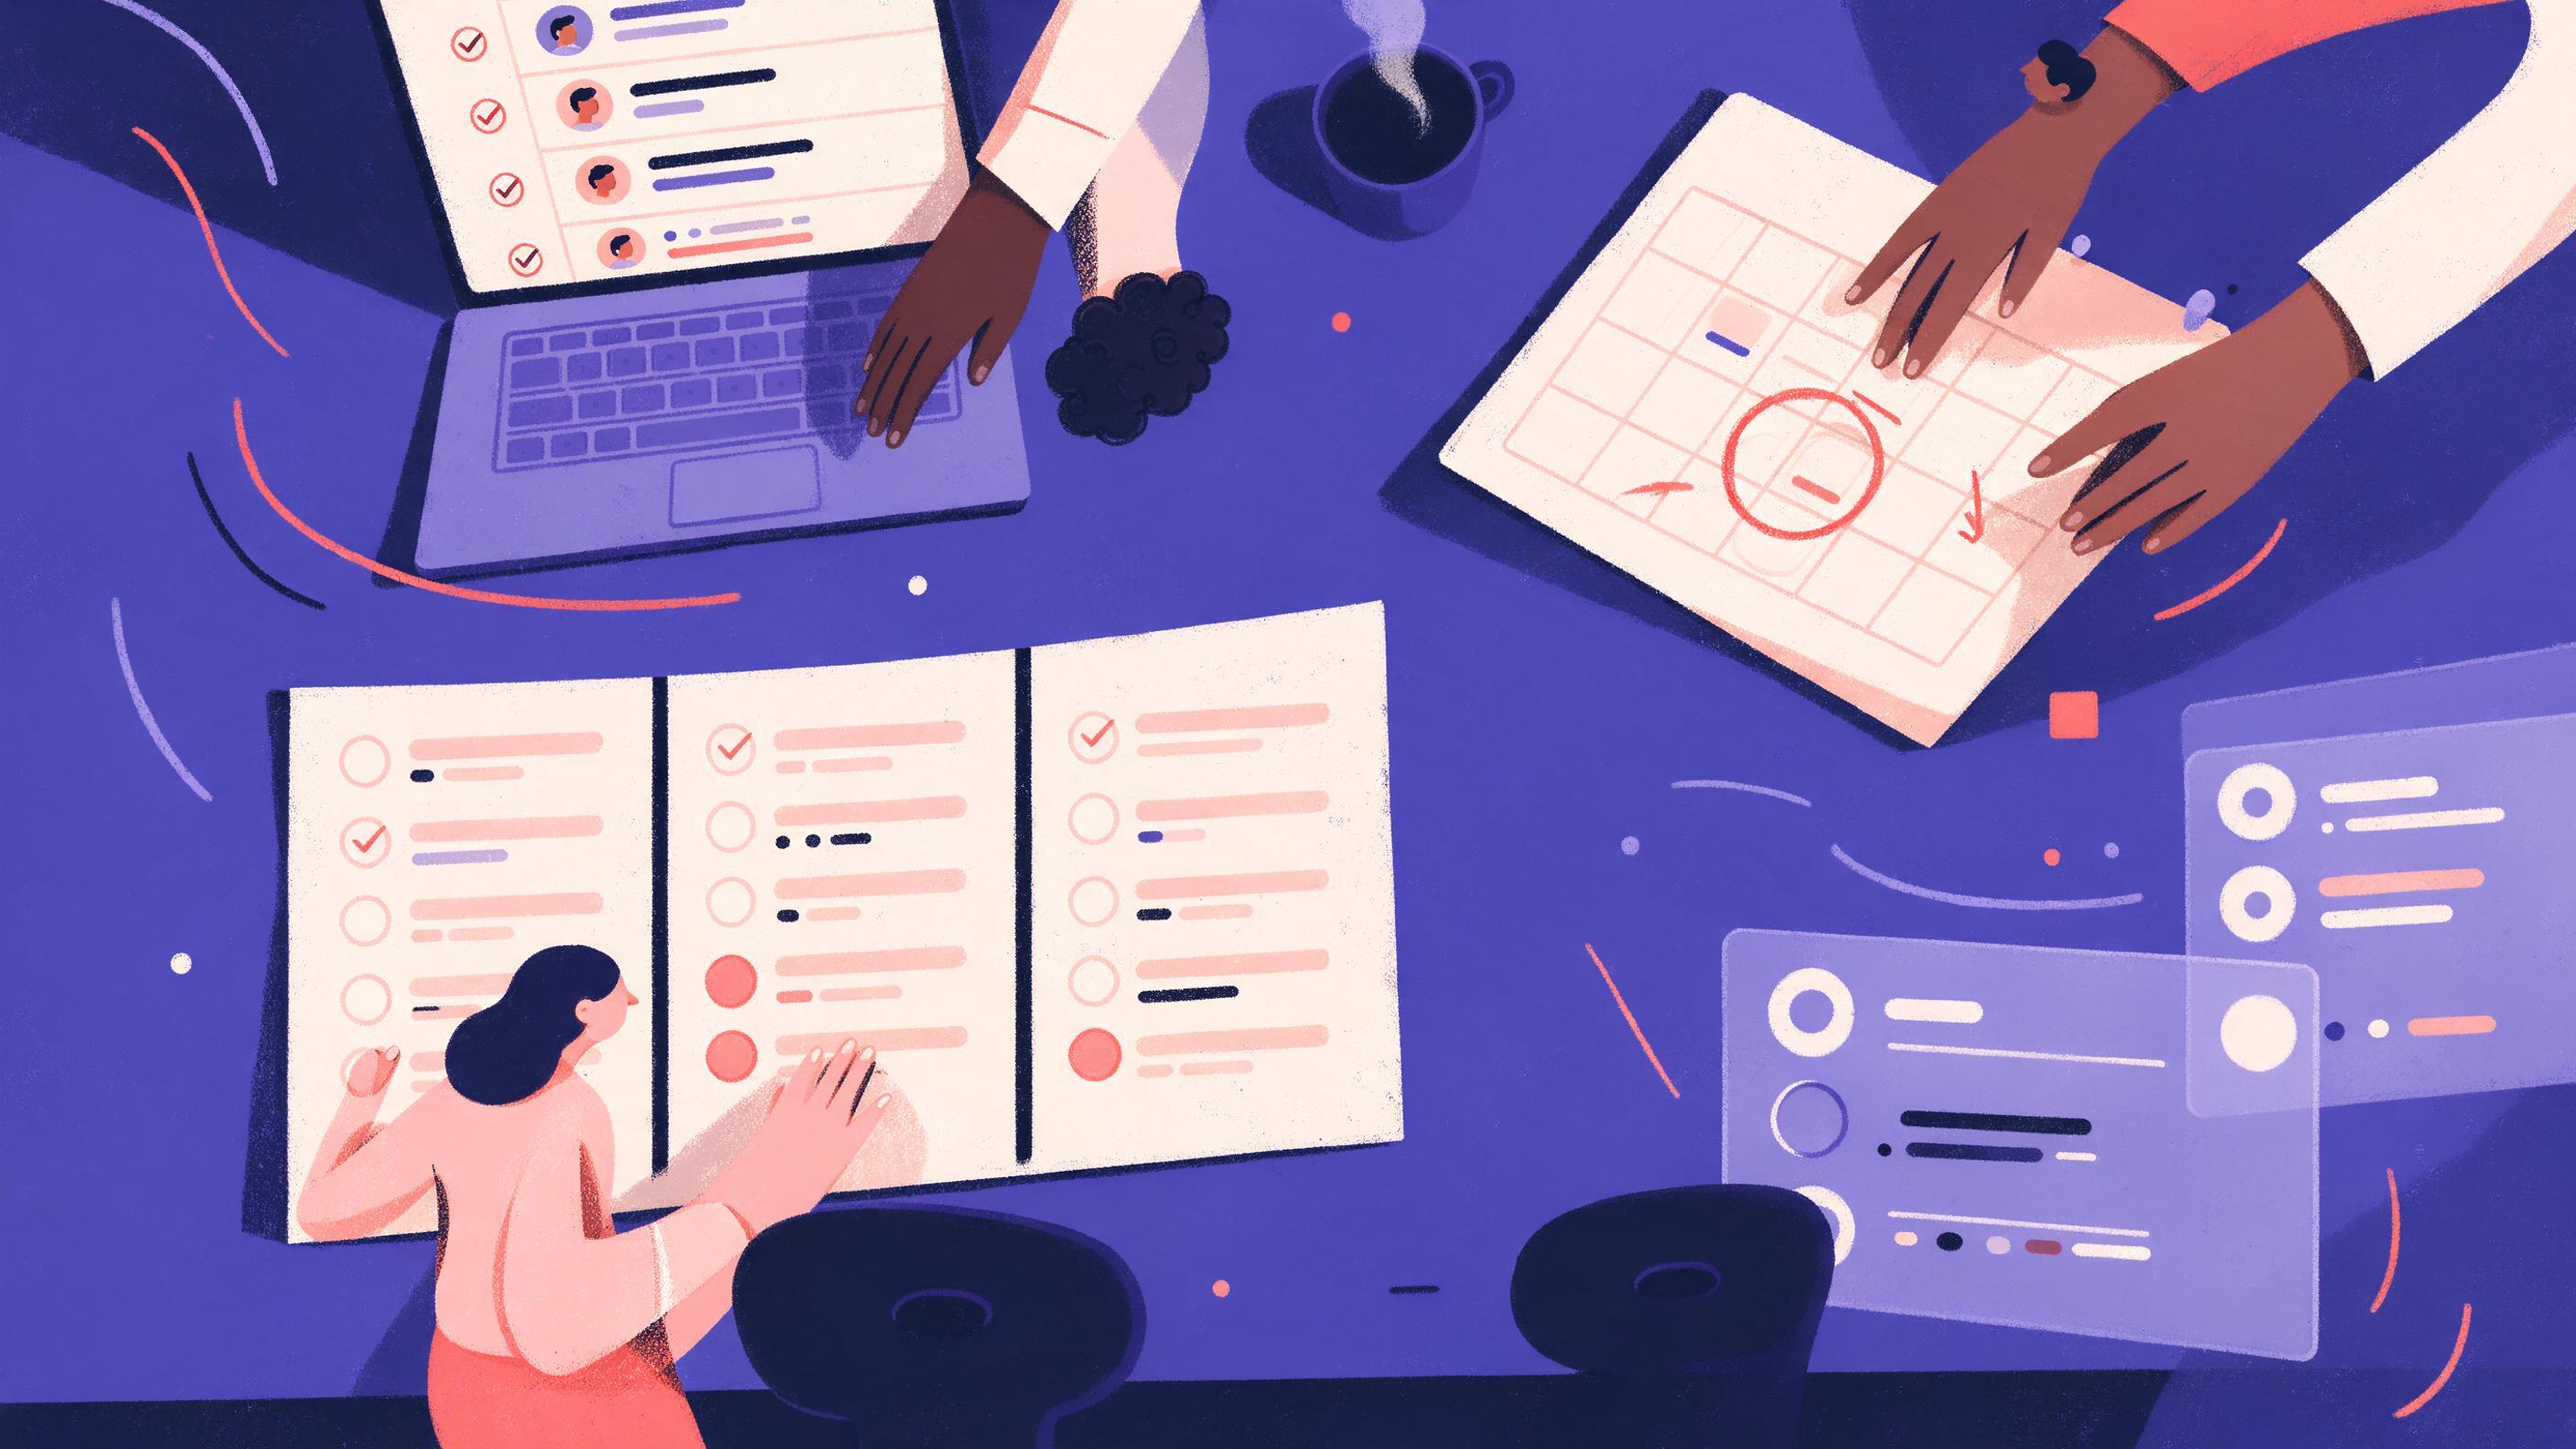
A top-down view of a desk with a printed checklist divided into three columns (keep, modify, revoke), a laptop showing an account list with checkmarks and owner names, a calendar with the review window circled in red.
Key points

Key points

  1. 1A quarterly access review works best as a fixed two-week window with one inventory sheet, a named business owner per row, and one keep, modify or revoke decision per account.
  2. 2The riskiest accounts sit outside your SSO export: local database users, cloud root and break-glass accounts, service accounts, API keys, and contractor logins.
  3. 3Every revoke and modify needs a ticket with a verified close date, because an unapproved review with no remediation trail is not evidence.
  4. 4Track orphaned accounts and time to revoke each cycle, and treat a rising count of departed employees with live accounts as an offboarding problem.

Why a fixed window beats an ad hoc cleanup

Most small teams do access cleanup whenever something falls over. That produces a review with no defined period, no consistent snapshot, and no way to compare one cycle to the next. The fix is boring: pick a review date, export every account as it exists on that date, and never edit the export with later changes. The export becomes the record for the quarter, and next quarter's export becomes a comparison point.

Frameworks treat this as a measurement problem rather than a one-time configuration task. The OWASP Software Assurance Maturity Model (SAMM) is built to give organizations an effective and measurable way to analyze and improve security practice, and it is explicitly risk-driven because there is no single recipe that works for every organization OWASP SAMM. That framing suits small teams: you are not satisfying an auditor's full checklist, you are establishing a baseline you can improve against.

There is a sharp warning in practitioner literature about mistaking documentation for reality. A widely quoted paragraph from a startup security list says SOC2 is about documentation, not reality, because the audits are performed by accountants rather than penetration testers Hacker News discussion. A small team can easily produce a beautiful sheet certifying access nobody checked. This procedure is designed to make the sheet match reality, which is harder and more useful.

Two weeks is long enough for owners to respond and short enough that the snapshot stays roughly accurate. Anything longer and people join, leave, or switch roles mid-review, so decisions apply to a state that no longer exists. Anything shorter and owners ignore the request until the deadline passes.

Step 1: Build the account inventory from four sources

The inventory is the whole game. If the list is incomplete, every later step is theater. Work outward from the identity provider, because it is the easiest source to export and usually covers the most accounts.

Source one: the SSO provider. Export the full user list with status, last login, assigned applications, and role. This is the bulk of your human accounts. Keep suspended users in a separate tab, because suspended accounts are the ones that get reactivated by mistake.

Source two: cloud consoles. Any team running production workloads should have audit logging on from the start; the same startup security discussion puts it bluntly, noting that if you are hosting in AWS you basically have to turn CloudTrail on and collect the data Hacker News discussion. For the review you need the IAM user and role list plus console access history. Service accounts and machine roles belong here even though no human logs into them.

Source three: databases and internal tools. Local database users, admin consoles, internal dashboards. These usually sit outside SSO and are the highest-risk, least-reviewed accounts.

Source four: third-party tools added by hand. Marketing platforms, analytics, support desks, design tools, and anything a department head bought on a credit card. Walk the finance system's vendor list, because it catches tools nobody thought to mention.

CISA's guidance for small business leaders makes inventory a leader action, not just an IT chore: learn what is on your network and maintain inventories of hardware and software assets so you know what is in play and at risk from attack CISA Cyber Essentials. The same logic applies to accounts, since an account you do not know exists cannot be reviewed or revoked.

A practical shortcut for manual sources: ask each department head for the last twelve months of tool invoices, then reconcile that list against SSO application assignments. Every vendor on the invoice that does not appear behind SSO is a manual row.

Step 2: Put every account in one sheet with the right columns

One spreadsheet, one row per account per system. A person with accounts in five systems gets five rows, because the keep, modify or revoke decision differs per system. These columns are the minimum that makes the sheet usable as both a working document and evidence.

ColumnPurposeExample value
Account identifierWho or what holds the account[email protected]
SystemWhich application or platformProduction database
Account typeHuman, service, shared, contractor, break-glassService
Current role or permissionThe actual privilege levelRead-write, no DDL
OwnerNamed business owner accountable for this accessHead of Data
Last activity dateWhen the account last authenticated or was usedExport date
DecisionKeep, modify or revokeModify
New permission if modifiedThe target stateRead-only
TicketLink to the remediation ticketENG-4412
Closed dateDate the ticket was verified completeBlank until done
NotesJustification or reasonUsed by nightly ETL job

Two design rules keep the sheet usable. First, the owner column must name a person, never a team name, because "Data Team" will not answer an email. Second, do not include passwords, tokens, or copies of personal data; store a reference to where evidence lives instead, a principle a public offboarding template states explicitly when it asks teams to keep evidence references rather than credentials or copied personal data Elba offboarding checklist.

Access review templates from compliance vendors converge on a similar field set: user identification, application inventory, access level, access start date, and a decision with a named approver SecureNDS access review template. An hour spent reading a few is worth it, because those fields have been shaped by audit findings you have not had yet.

Step 3: Assign a business owner to every row and force the three-way decision

The core question per account is not "does this look fine" but "who says so, and on what date." A free template frames it as three questions per account: should this person still have access at all, is the level of access still right, and who approves it with a name and a date SecureSlate access review template. Small teams skip the third question, and it is the one that turns a spreadsheet into evidence.

Owner assignment follows one rule: the owner is the person who would notice if the access were misused. For production databases, that is the engineering lead. For the CRM, the head of sales. For the finance system, whoever owns the books. For service accounts, the engineer who wrote the job that uses them.

Send each owner a filtered view containing only their rows, with three permitted answers:

  • Keep: the account is needed, the permission level is correct, and the owner's name goes in the approver column with the review date.
  • Modify: the account is needed but over-privileged. The owner must specify the target permission, not just say "reduce," because vague instructions produce vague tickets.
  • Revoke: the account is not needed. The owner states why, in one line.

The decision rule that saves the most argument: if an owner does not respond by the deadline, the default is revoke for accounts with no activity in the review period and keep for accounts with recent activity. Announce this default at the start of the window. It converts a polite request into a deadline with consequences, and silence never leaves a dormant account alive.

Two categories deserve a second look whatever the owner says: any account with administrative or root privileges, and any account belonging to someone who has left, changed team, or finished a project. Admin granted for a one-off migration that ended months ago is the classic finding SecureSlate access review template. Ask the owner directly whether that migration still runs.

Step 4: Run the review on a calendar, not on goodwill

A repeatable process has dates that do not move. Put the cycle on a calendar and let the calendar drive the work. This table is one quarter; repeat it with shifted dates.

DayActivityOutput
Day 1 (Mon)Freeze the review date, export all automated sourcesRaw exports
Day 2Add manual sources, reconcile vendor invoicesDraft inventory sheet
Day 3Assign business owners to every rowOwner column complete
Day 4Send each owner filtered rows, answer key and default ruleOwner packs sent
Day 10 (Fri)Deadline for owner decisionsDecisions recorded
Day 11Apply no-response default, spot-check admin and departed rowsFinal decision column
Day 12Open one ticket per modify and revokeTicket queue
Day 14Verify closures, record closed dates, archive the sheet, schedule next windowEvidence file and calendar entries

Two things make this schedule work in a company of five to fifty people. The IT lead's total effort is roughly four half-days, small enough to defend against competing priorities. Owners spend minutes, not hours, because they receive only their rows and a three-option answer key.

If the review keeps surfacing departed employees with live accounts, resist moving to monthly reviews. The review is detective, not preventive, and it is doing its job by catching what offboarding missed. Fix the offboarding instead, starting with a confirmed departure date, a full inventory beyond the identity provider, and verification that sessions and tokens have stopped working rather than only that new sign-ins are blocked Elba offboarding checklist.

Step 5: Close the loop with tickets, dates and two metrics

A review that ends with a spreadsheet edit ends with nothing. Every modify and revoke needs a ticket in the system your team already watches, plus a recorded close date after someone verifies the change in the source system.

The ticket carries four things: account identifier, system, target state (the exact new permission or full removal), and who requested it. When it closes, someone signs in to the source system, confirms the change took effect, and writes the date back into the sheet. Verification by inspection matters because a revocation request is not a revocation. Blocking a sign-in does not stop a session or token from working, as offboarding guidance notes explicitly Elba offboarding checklist.

Then record two metrics per quarter in the sheet header so they are visible next cycle:

  1. Orphaned accounts: rows whose owner has left the company, or whose account shows no activity across two consecutive reviews and was not revoked. Count them and list them by name in an appendix.
  2. Time to revoke: the median days from decision to verified closure for revoke decisions. Track the maximum too, because one account that took six weeks tells you more than a good median.

A third metric is optional once you have history: the percentage of rows where the owner changed the decision from the previous cycle. Rising churn suggests roles shift faster than provisioning follows. A flat zero across several cycles suggests owners are rubber-stamping, which is its own warning sign.

Small businesses are not a low-risk category. Huntress cites the Verizon Data Breach Investigations Report finding that small businesses under 1,000 employees suffered 2,842 confirmed data breaches compared with 751 at large enterprises Huntress small business checklist. Misused credentials remain a persistent entry path, and the review is one of the few controls that actively retires them.

The checklist you can hand to a new IT hire

Print this. It is short enough to finish in the two-week window and specific enough that someone who has never run a review can follow it.

#CheckDone when
1SSO user and application export captured on the review dateDated export file saved
2Cloud IAM users, roles and service accounts exportedDated export file saved
3Database and internal admin users listed by handRows added to sheet
4Third-party tools reconciled against vendor invoicesEvery vendor mapped to SSO or added as a row
5Every row has a named owner who is a personNo team names in owner column
6Owner packs sent with answer key and default ruleSend date recorded
7Every row has a decision, or fell to the defaultDecision column complete
8Admin, root, break-glass and departed-employee rows spot-checkedNotes column shows the check
9One ticket per modify and revoke, including target stateTicket links in sheet
10Each closed ticket verified in the source systemClosed date in sheet
11Orphaned accounts and time to revoke recordedHeader of next sheet
12Sheet archived in an approved location, next window scheduledBoth done the same day

Expect the first cycle's inventory to overrun the schedule, because you will discover accounts nobody knew about. That is the point. A first review that finds dozens of orphans is a successful review, and the second should find far fewer. Most frameworks encourage exactly this incremental pacing rather than a single big-bang cleanup; NIST's Secure Software Development Framework is built as a set of practices to integrate into existing work, adaptable to an organization's existing methodology and risk profile NIST SSDF.

One structural decision remains: who runs the review, and who checks the runner. In a small team the person running the review usually holds admin access to everything being reviewed, which is the situation the review exists to catch. Add one line: a second person, typically the operations lead, reviews the reviewer's own rows and signs the archive. That single step closes the most embarrassing gap in a small team's access review.

FAQ

FAQ

How long should a quarterly access review take?

Budget two weeks from export to archived evidence, with roughly four half-days of actual IT effort spread across the window. The remaining elapsed time is owner response time, not work. Compressing below a week usually produces unanswered owner requests, and stretching past three weeks means the snapshot no longer matches reality.

What should happen if a business owner does not respond?

Apply the default announced at the start of the window: revoke accounts with no activity in the review period, keep accounts with recent activity, and note the default in the decision column. This stops silence from leaving dormant access alive and gives owners a reason to answer next quarter. Send one reminder per cycle, not individual chasing.

Should service accounts and API keys be in scope?

Yes, and they deserve their own rows. Service accounts and CI tokens are the accounts nobody offboards, because they do not leave the company, and they often hold broader access than any human SecureSlate access review template. Assign each to the engineer who wrote the job using it, and revoke any whose job no longer runs.

How do I handle contractors and vendor support accounts?

List them with an explicit contract end date and review them every quarter without exception. Contractor accounts sit outside the usual offboarding trigger, so the calendar is the only thing that retires them. Treat an expired contract with a live account as an orphan and count it in your metric.

Is a spreadsheet enough, or do we need access review software?

A spreadsheet is enough for most teams under fifty people, provided each row has a named owner, a decision, a ticket link and a verified close date. Software earns its cost when in-scope systems number in the dozens and manual exports take more than a day. Before then, the discipline of a fixed window matters more than the tool.

Sources

Sources

  1. OWASP SAMM
  2. Ask HN: IT Security Checklist for Startups? - Hacker News
  3. Cyber Essentials | CISA
  4. Employee offboarding checklist: SaaS access template | Elba
  5. Ultimate User Access Review Template: Key Components
  6. Free Access Review Template (Excel)
  7. Small Business Network Security Checklist: 12 Essential Steps
  8. Secure Software Development Framework (SSDF)
About the author

About the author

Antonio Evans
Antonio Evans

Antonio Evans is the founder of Quanta Intelligence and a fractional CTO who builds HIPAA-ready AI systems for health and life-science companies. Before that he was technical co-founder of FriendsEAT for twenty years, CEO of Socialdraft, and a data engineer at IBM. Antonio lives with his dog Santino in Lisbon, Portugal.

All articles